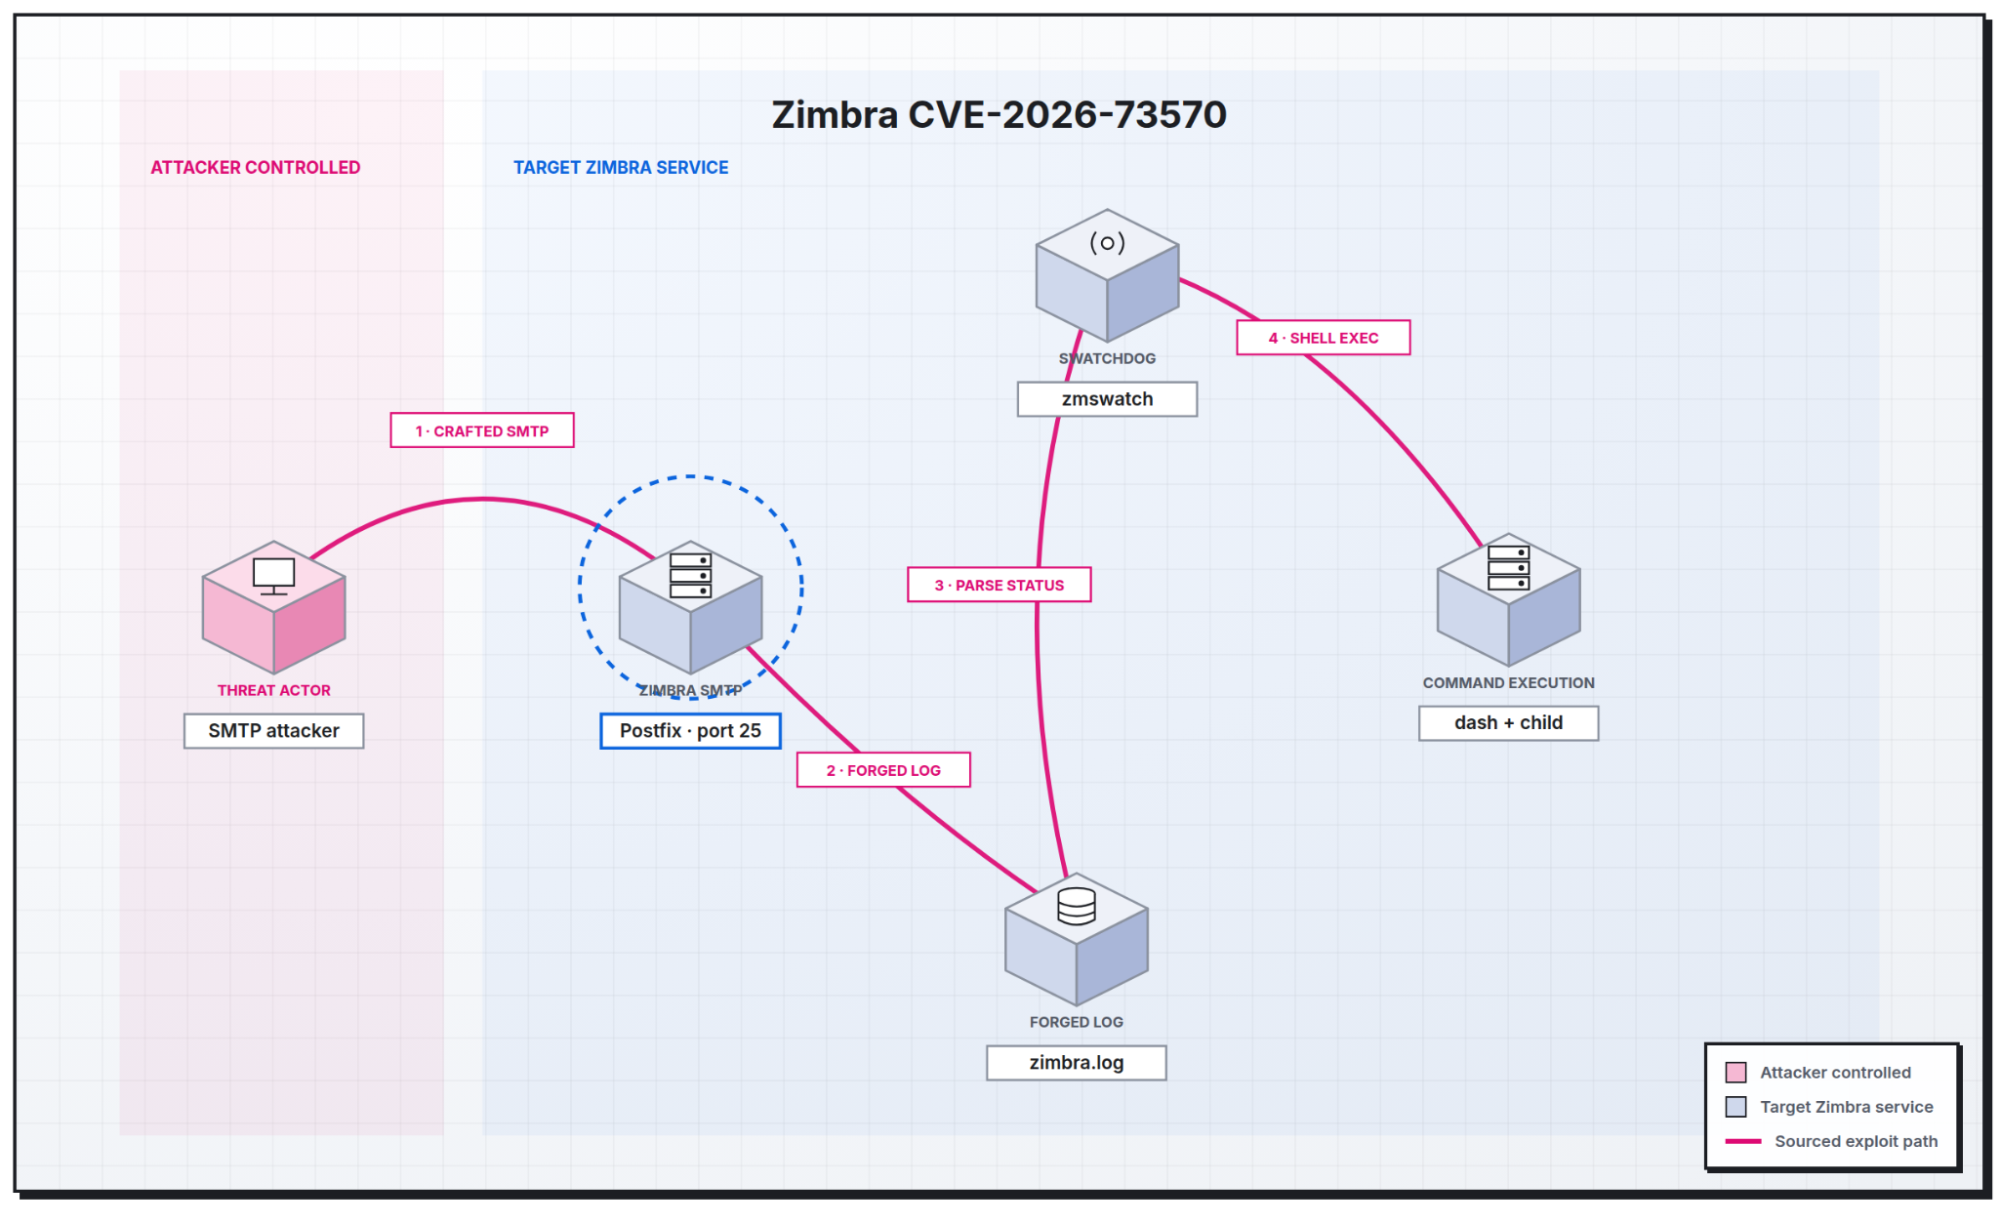
How CVE-2026-73570 turns a Zimbra log file into remote code execution
We reproduced the Zimbra command injection vulnerability and found that several public PoCs write a payload Swatchdog never matches, so a failed test looks like a patched server.
php2shell: Assessing Elastic detection coverage relevant to CVE-2026-109618 and CVE-2026-109619
CVE-2026-109618 and CVE-2026-109619 are critical PHP core RCE flaws that leaked ahead of disclosure. We cover what is verified, why exploitation converges on a web server spawning a shell, and the Elastic detections developed to catch this behavior.
Auditing the auditor: Unmasking Apex Accelerator
REF8801 exposes how Apex Accelerator combines convincing Web3 services with malicious npm packages, attacker-controlled AI infrastructure, and cross-platform malware delivery.
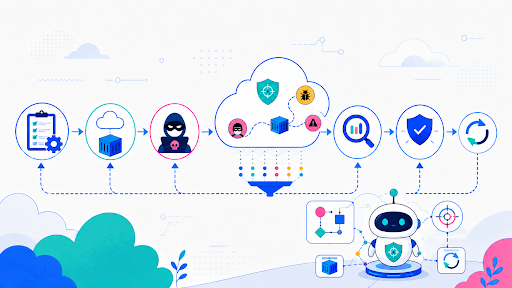
Cloud Threat Emulation on Autopilot: Context is Everything
Cloud threat emulation is more than detonation. A plan-first methodology for cloud detection engineering: scope, victim model, telemetry, coverage, cleanup. Learn how to properly leverage AI to automate your emulations.
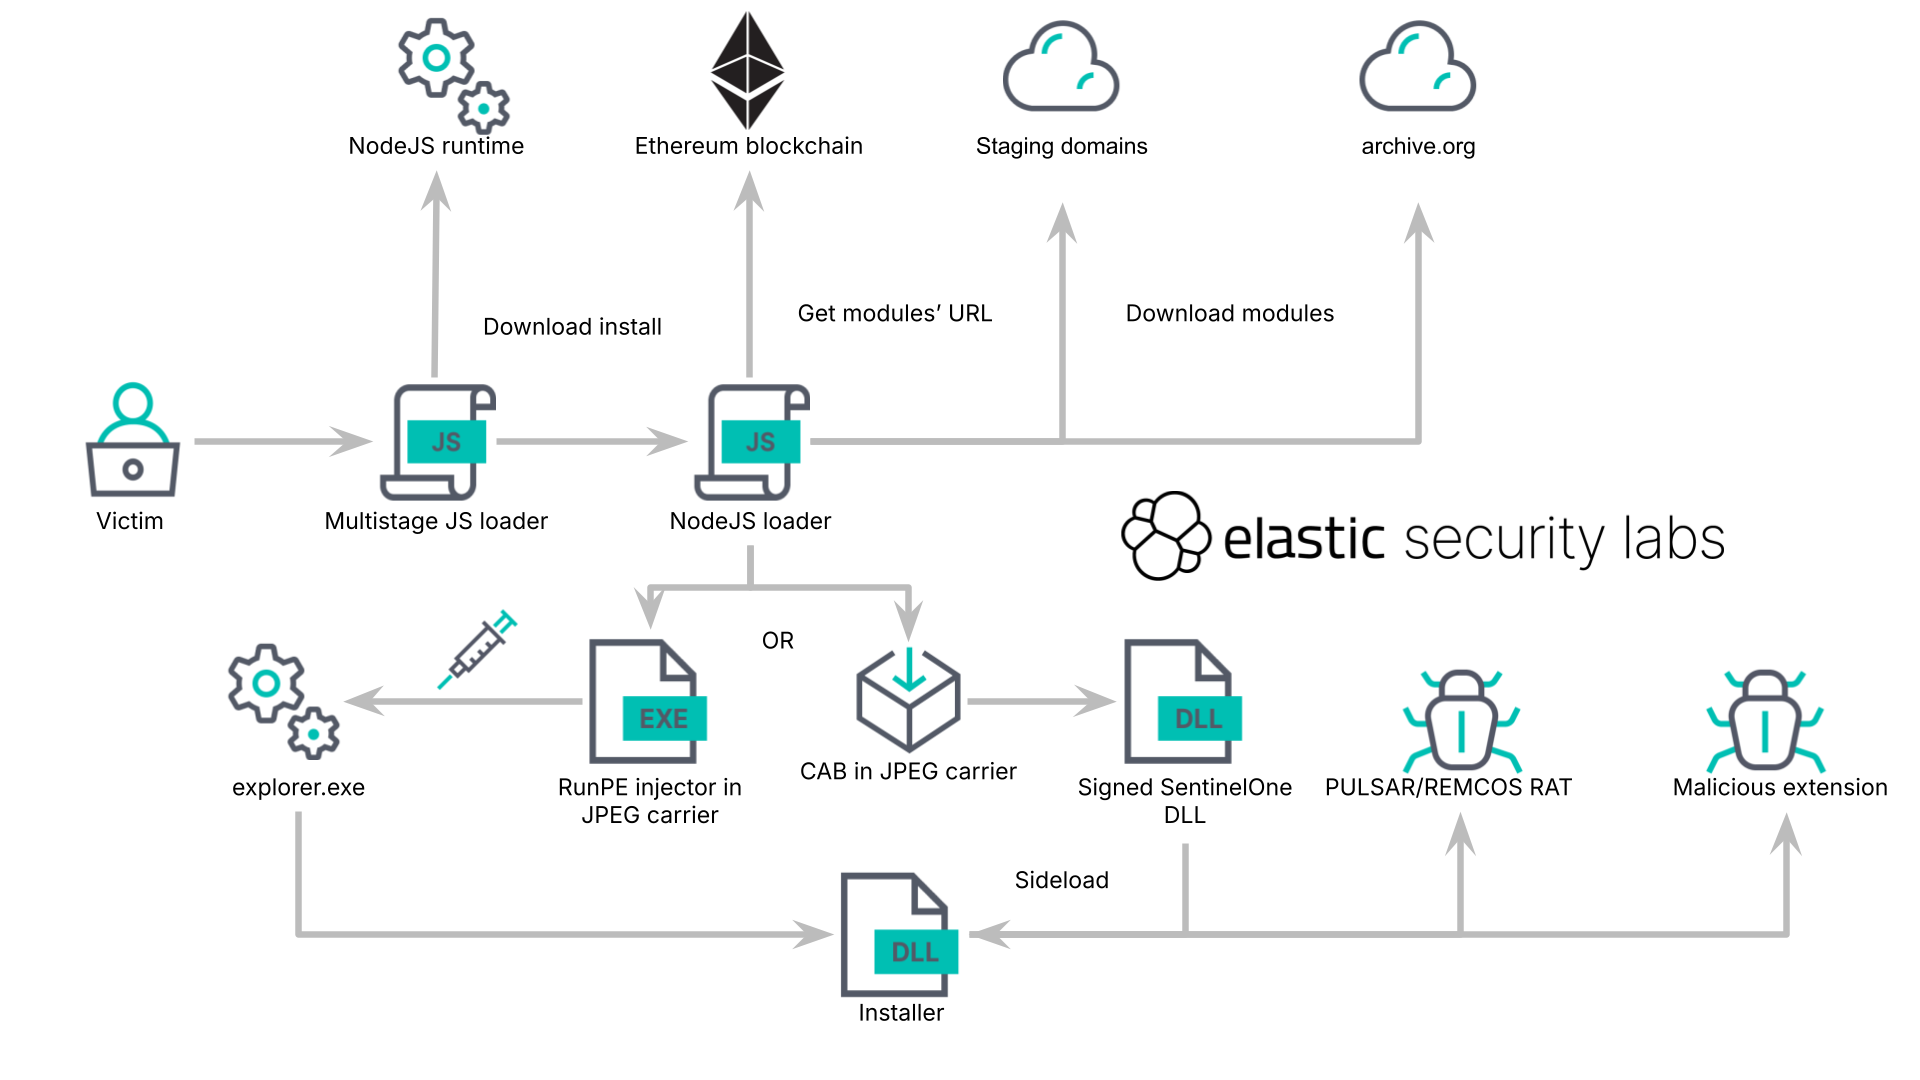
The extension you never installed: KREMLIN forges Chrome's own integrity checks to steal banking sessions
Elastic Security Labs tracked this malicious browser extension across seven campaigns and 15 months, through Brazilian bank lures and the Ethereum smart contracts that hold its C2 configuration.

Linux Detection Engineering - Local Privilege Escalation
Seven of the thirteen Linux privilege escalation CVEs we tracked in 2026 turned out to be the same copy-on-write bug pointed at different kernel interfaces. We ran the public proof-of-concept for eleven exploits and two misconfigurations, and noted which rules fired.
How to correlate Kubernetes audit logs with container runtime data
Two fields join the Kubernetes API to what ran inside the pod, and one turns up a container escape your process events never recorded.
REVSTEALER ramps up: analysis of up-and-coming infostealer
Elastic Security Labs deep dives into REVSTEALER, an emerging infostealer targeting browsers, wallets, and gaming accounts.
Linux Detection Engineering - Fileless Execution
We reproduced five Linux fileless execution patterns with FENIX, including memfd_create staging, interpreter one-liners, deleted binaries, and in-memory kernel module loads, then mapped each to the Elastic Defend rules that catch it.
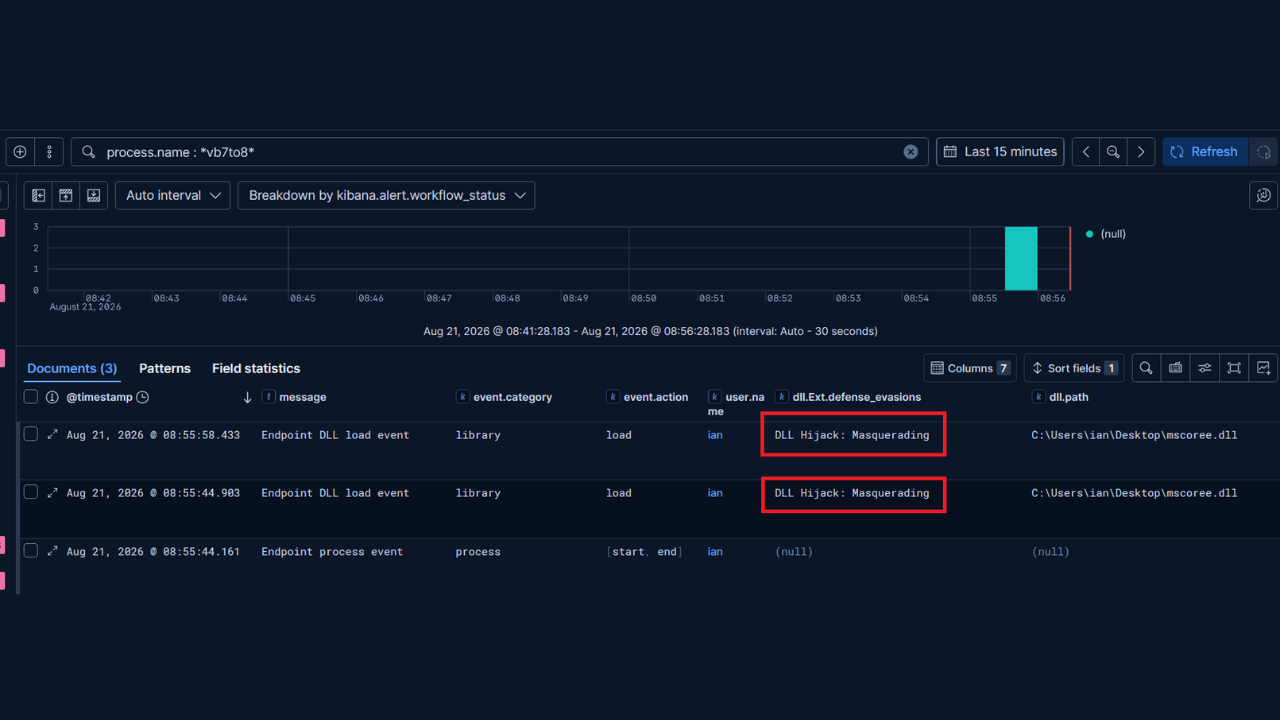
From 88 lines to 1: Detecting DLL hijacking with Elastic Defend
The ClickFix campaign that sideloads a malicious mscoree.dll also ships a driver to kill Elastic Endpoint. We rebuilt that DLL as a NativeAOT library, dropped it beside a signed Microsoft binary, and Elastic Defend 9.5.0 flagged the load.
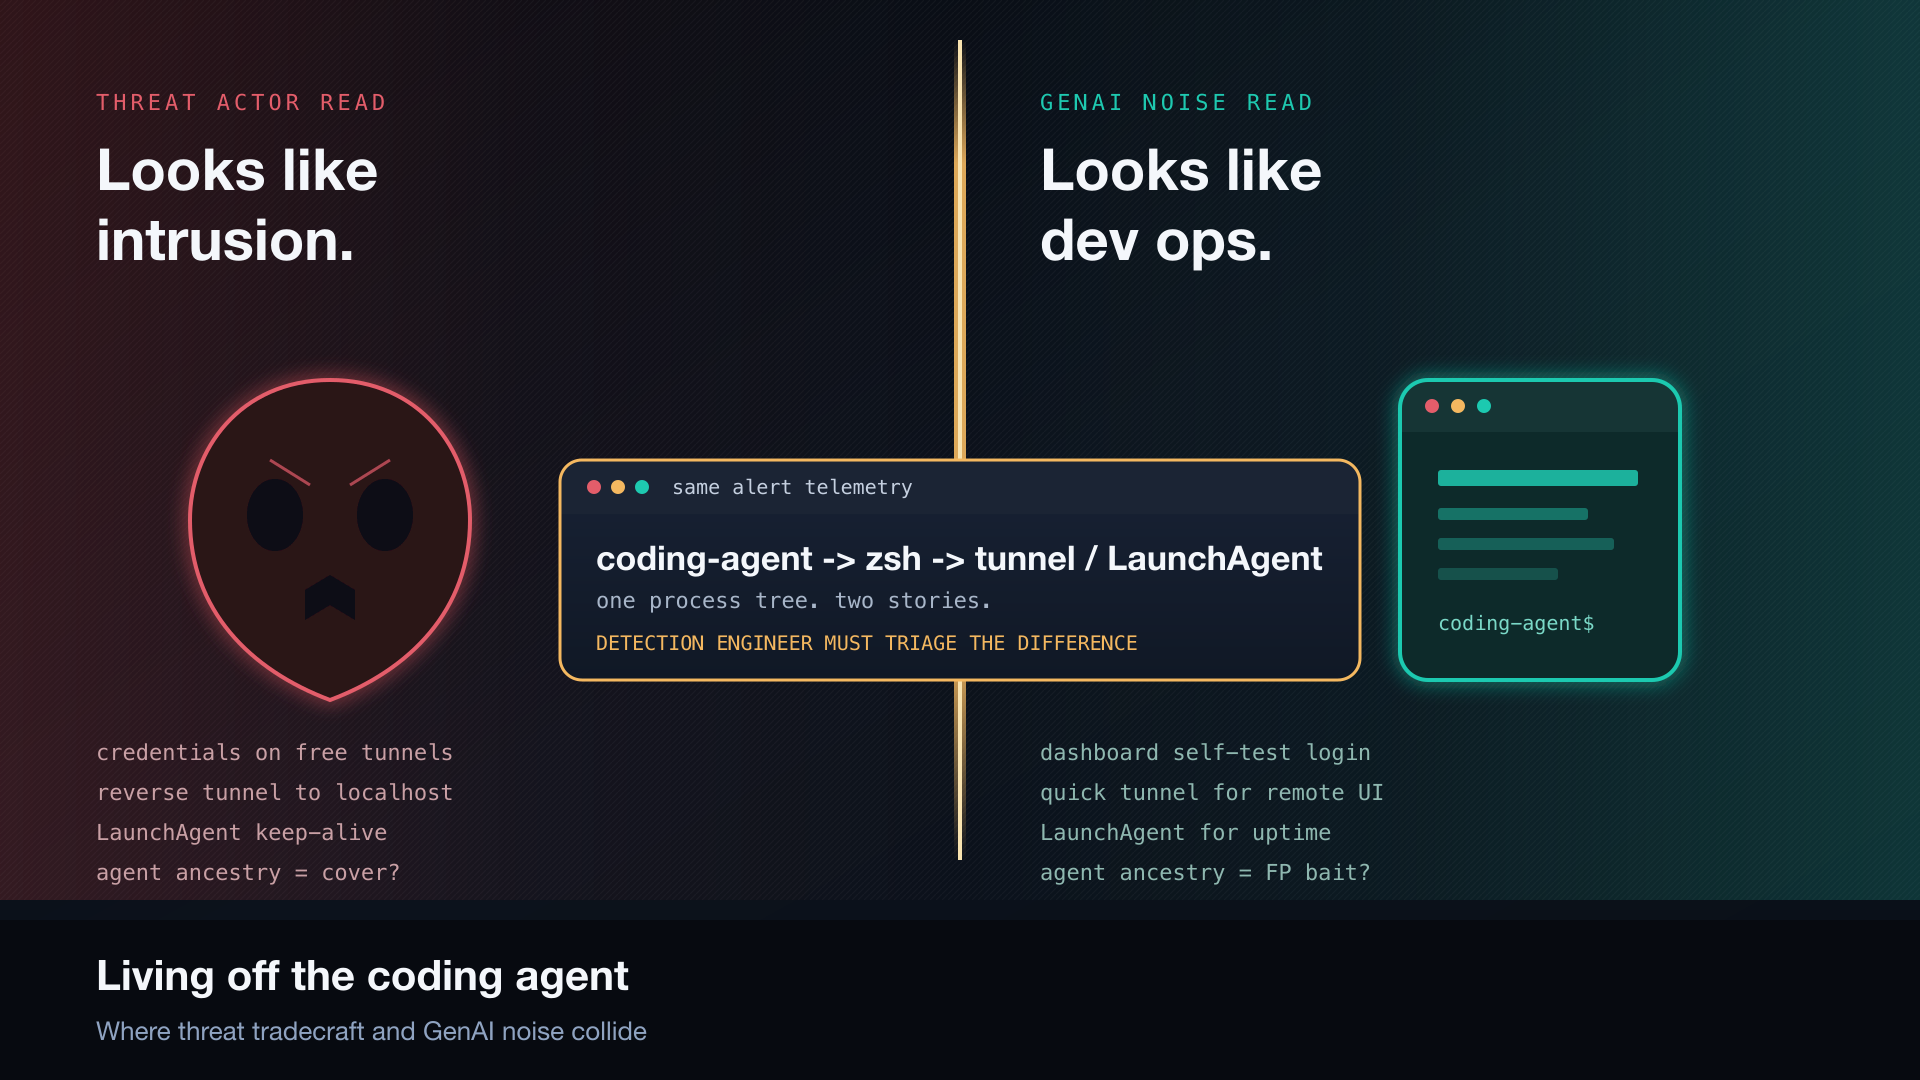
Living off the coding agent: Two tales of tunnels and LaunchAgents
Agent-parented reverse tunnels and LaunchAgents can expose a local admin app to the internet. Endpoint still needs to treat that as high severity even when the activity looks like vibe-coded ops, not confirmed malware.
Shai-Hulud strikes again: CHAINDROP worm hits 400+ npm packages
Elastic Security Labs identified the return of Shai-Hulud. Attackers compromised the keyv maintainer and deployed CHAINDROP, a worm that uses stolen npm credentials to backdoor co-owned packages totaling over 1.3 billion monthly downloads.