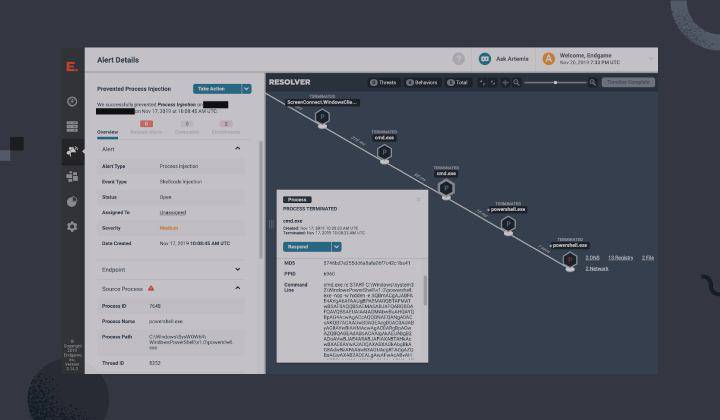
Ransomware, interrupted: Sodinokibi and the supply chain
Learn how Elastic Endpoint Security's behavior-based protections prevented a targeted ransomware attack on multiple endpoints.
Okta and LAPSUS$: What you need to know
The latest organization under the microscope of the LAPSUS$ group is Okta. Threat hunt for the recent breach targeting Okta users using these simple steps in Elastic
Nimbuspwn: Leveraging vulnerabilities to exploit Linux via Privilege Escalation
Microsoft 365 Defender team released a post detailing several identified vulnerabilities. These vulnerabilities allow adversarial groups to escalate privileges on Linux systems, allowing for deployment of payloads, ransomware, or other attacks.
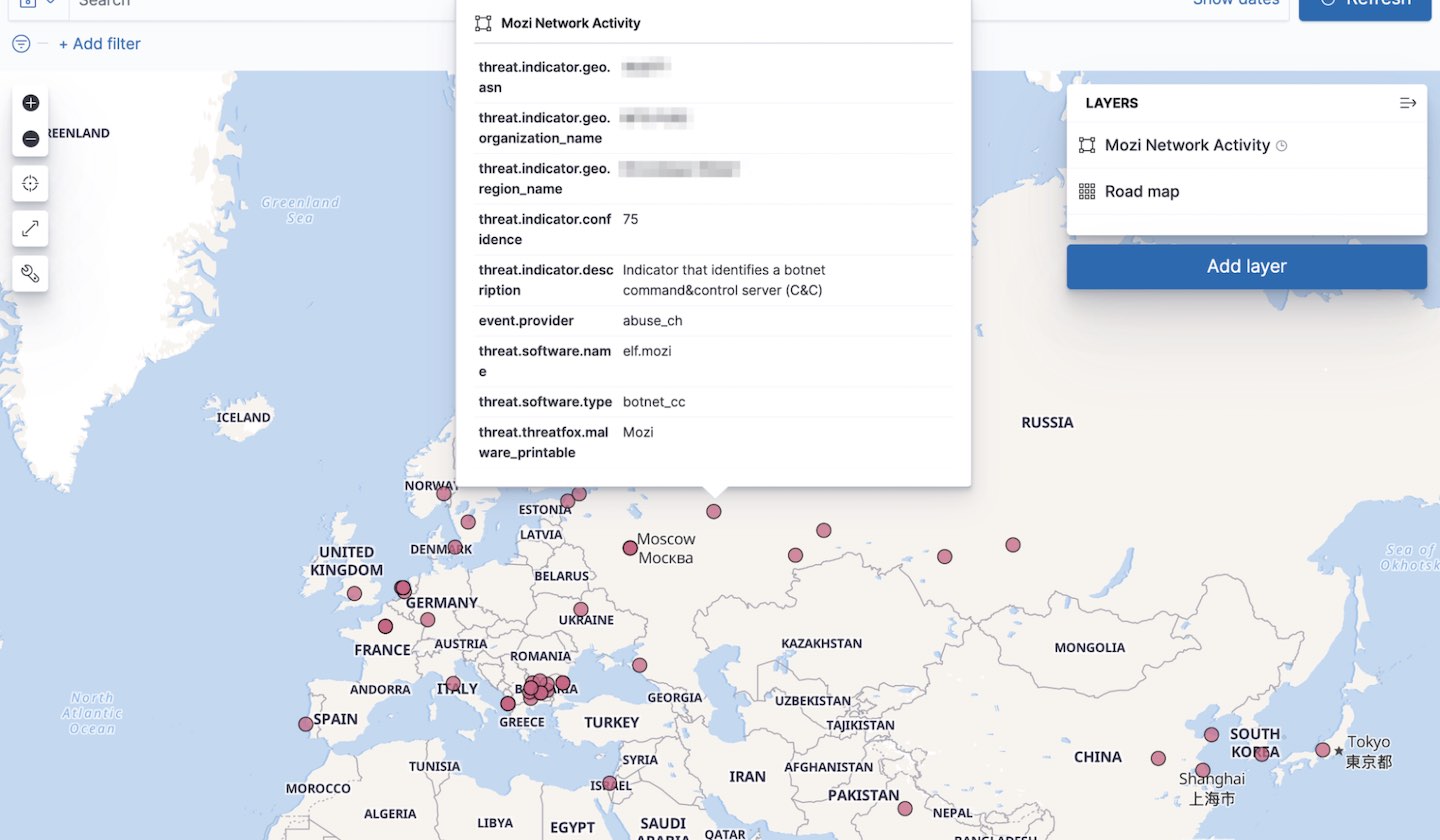
Collecting and operationalizing threat data from the Mozi botnet
The Mozi botnet is an ongoing malware campaign targeting unsecured and vulnerable networking devices. This post will showcase the analyst journey of collecting, analyzing, and operationalizing threat data from the Mozi botnet.
Testing your Okta visibility and detection with Dorothy and Elastic Security
Dorothy is a tool for security teams to test their visibility and detection capabilities for their Okta environment. IAM solutions are frequently targeted by adversaries but poorly monitored. Learn how to get started with Dorothy in this post.
Practical security engineering: Stateful detection
By formalizing stateful detection in your rules, as well as your engineering process, you increase your detection coverage over future and past matches. In this blog post, learn why stateful detection is an important concept to implement.
Embracing offensive tooling: Building detections against Koadic using EQL
Find new ways to build behavioral detections against post-exploitation frameworks such as Koadic using Event Query Language (EQL).